
Category: Kubernetes
-
Controlling upstream HTTP versions in NGINX Ingress Controller
If you run microservices in Kubernetes, NGINX Ingress Controller talks to your backend pods using HTTP/1.1 by default. For most web apps, HTTP/1.1 is fine. But more backend services now accept HTTP/2 without TLS (h2c), which multiplexes many requests over one connection. Some older backends still need HTTP/1.0. (gRPC backends were already covered: nginx.org/grpc-services and…
-
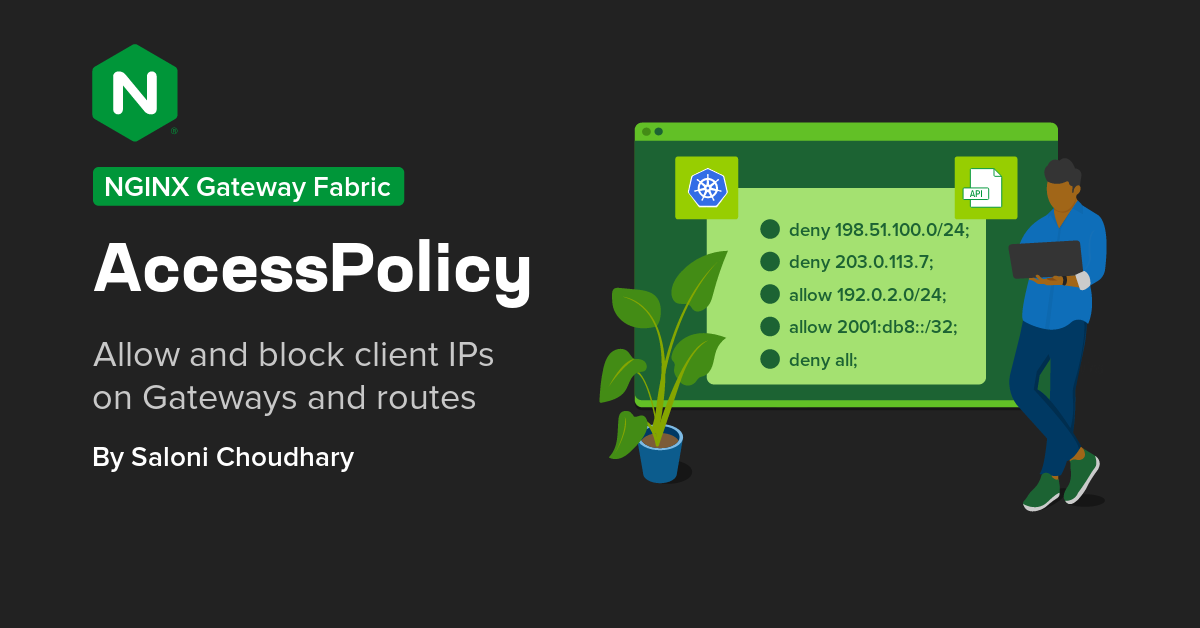
Allow and block client IPs in NGINX Gateway Fabric with AccessPolicy
AccessPolicy in NGINX Gateway Fabric lets you allow or block client IP addresses and CIDR ranges on a Gateway or on individual routes. If you already use NGINX Gateway Fabric to manage traffic into your cluster, you can now control which clients reach your apps in the same place, with a policy attached to the…
-
I asked my agent for a Kubernetes cluster. It built me Buubernetes complete with NGINX Gateway Fabric. Your agent can do it to.
I rate my NGINX skills as basic. I’ve done the normal things: web serving, reverse proxy and a few upstreams, some TLS. If something went sideways, I’d be learning the ins and outs on the fly. That’s great if you want to learn that, but I’m much more interested in evaluating architectures and building systems…
-
NGINX Gateway Fabric 2.8: IP allow and deny lists, passive health checks, and cookie-based session persistence
NGINX Gateway Fabric 2.8 adds AccessPolicy, which allows or denies traffic to a Gateway or route by client IP address. Passive health checks in UpstreamSettingsPolicy let you decide how many failed attempts take an upstream server out of rotation and for how long, and cookie-based session persistence now works on NGINX Open Source. NGINX Gateway…
-
NGINX Ingress Controller 5.7: HTTP/2 to your upstreams, Opaque Secrets, and cert-manager challenges behind HTTPS redirects
NGINX Ingress Controller 5.7 speaks HTTP/2 to your upstream services, set per upstream or picked up from a Service’s appProtocol. An Opaque Secret now works anywhere a TLS, CA, htpasswd, or API key Secret does, so you can use a Secret created by other tooling as it is. HTTP-01 challenges from cert-manager complete on hosts…
-
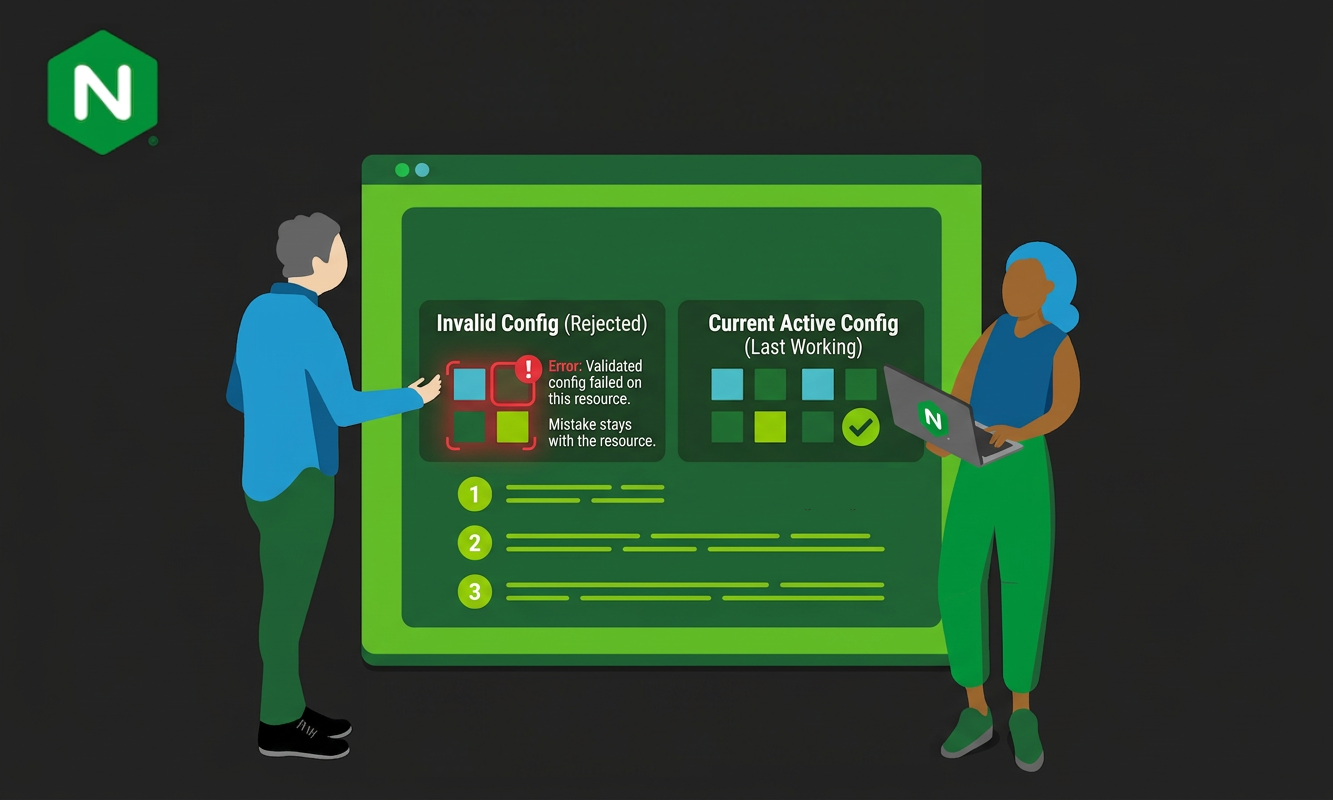
How Config Safety Protects NGINX Ingress Controller from Invalid Configuration
NGINX Ingress Controller turns Kubernetes resources into NGINX configuration. Many of those inputs are free-form text: snippet annotations on Ingresses, snippets on VirtualServers, and in the global ConfigMap. A typo in any of them can produce configuration that NGINX refuses to load. Config safety makes sure such a mistake stays with the resource that introduced it. Configuration…
-
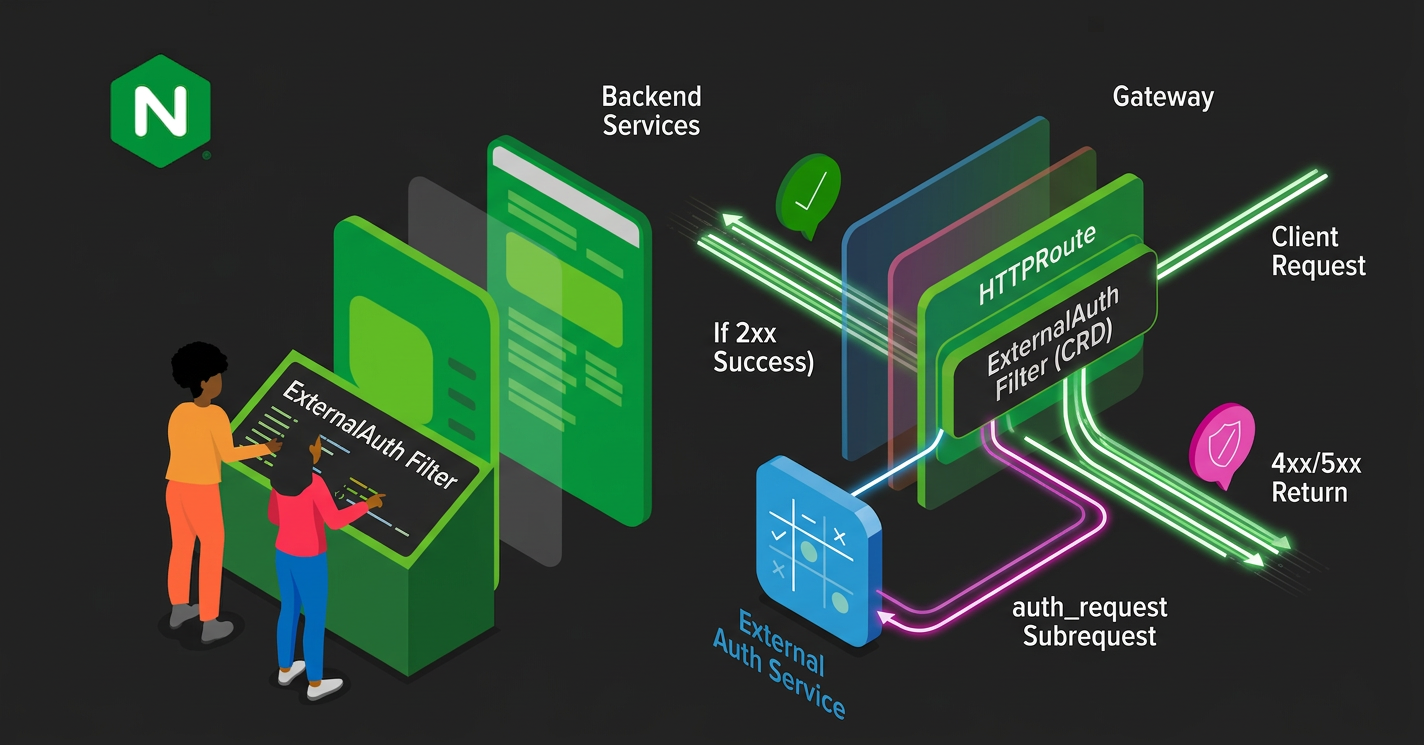
Stop Writing Authentication Checks Into Every Service. Combine Them in your Kubernetes Gateway.
If you run a platform with a dozen or more services behind it, you’ve probably seen this pattern. Service A checks an API key. Service B calls out to your identity provider directly. Service C has a half-finished authentication middleware that hasn’t been touched in a while. Every team solved the same problem differently, and…
-
HTTP Strict Transport Security Policy in NGINX Ingress Controller
NGINX Ingress Controller 5.6.0 introduces HSTS as a Policy type for the VirtualServer CRD. This blog gives a quick overview of the feature with some deployment examples and tips on how to correctly configure this policy. Across this blog, we’re focused on: What is HSTS? HTTP Strict Transport Security (HSTS) is a security feature that…
-
NGINX Gateway Fabric 2.7: Gateway API 1.6 conformance, external authentication, and fewer snippets
NGINX Gateway Fabric 2.7 is a significant release, targeting Gateway API conformance, data plane improvements, and workflow enhancements. TCPRoute and UDPRoute graduate to v1 with Gateway API 1.6, TLS listeners gain Terminate mode, and a new HTTPExternalAuthFilter calls out to an authorization proxy without an NGINX snippet. Seven more NGINX settings move out of snippets…
-
NGINX Ingress Controller 5.6: HSTS without snippets, a faster start on large clusters, and improved configuration safety
NGINX Ingress Controller 5.6 implements more support for configuring NGINX through resources instead of through snippets. HTTP Strict Transport Security (HSTS) becomes a first-class policy across VirtualServer, VirtualServerRoute, and Ingress. Two new annotations close configuration gaps for teams moving off Ingress-NGINX, and the X-Forwarded base headers can now be turned off through the ConfigMap. Operational…
-
External Authentication Policy in NGINX Ingress Controller: A Real World Use Case
NGINX Ingress Controller 5.5.0 introduced the ExternalAuth Policy. This is the second blog post in a two part series that covers the ExternalAuth Policy, and is focused on a real world use…
-

External Authentication Policy in NGINX Ingress Controller: Patterns for VirtualServer and Ingress
NGINX Ingress Controller 5.5.0 introduced the ExternalAuth Policy. This is the first blog post in a two part series that covers the ExternalAuth Policy, and is focused on how the policy…
-
mTLS Policies in NGINX Ingress Controller
NGINX Ingress Controller 5.5 brings full support for mTLS in Ingress objects! This blog post gives a more in-depth overview of our GitHub deployment examples and shows how to configure both our new ingress and egress mTLS Policy CRDs in NGINX Ingress Controller using annotations. Ingress mTLS Ingress mTLS configures how NGINX verifies client certificates…
-
Optimising NGINX Ingress Controller Startup Performance
NGINX Ingress Controller 5.5 introduces some significant performance improvements in startup times! A few months ago, a community member noticed that NGINX Ingress Controller deployments with a large number of Ingress resources were experiencing longer-than-expected startup times. In clusters with hundreds or thousands of resources spread across many namespaces, the controller could take several minutes…
-
Meet With Us: NGINX Gateway Fabric & NGINX Ingress Controller Community Calls
Connection, collaboration, and trust are the lifeblood of healthy community culture. NGINX Gateway Fabric and NGINX Ingress Controller were (and are) developed with open source community as a priority. From code contributions to critical comments, community participation has shaped the present and future of NGINX open source projects, and the future of technology. Today, I’m excited to highlight two recurring opportunities to engage directly…
-
NGINX Ingress Controller 5.5: Security, Performance, and Easier Migration
NGINX Ingress Controller 5.5 is a focused, community-driven release. It brings new capabilities, expanded Kubernetes Ingress support, a significant startup performance improvement at scale, and more annotations to ease migrations from ingress-nginx. Here’s what’s new. External Authentication for Ingress and VirtualServer What’s new?: External Authentication is now supported for both Ingress and VirtualServer resources. Based…
-
NGINX Gateway Fabric 2.6: F5 WAF for NGINX Comes to the Gateway API
NGINX Gateway Fabric 2.6 marks our initial foray into implementing enterprise grade security capabilities into the Gateway API standard. This release brings F5 WAF for NGINX support to a Gateway API implementation, making NGINX Gateway Fabric one of the first Gateway API implementations to offer enterprise-grade WAF capabilities natively. Here’s what else is new: F5…
-
Built for Change: How NGINX Ingress Controller and NGINX Gateway Fabric Handle Kubernetes Backend Changes Natively
Kubernetes applications are designed to change constantly. Pods scale out, roll forward, restart, and disappear, so the traffic layer has to keep pace with a backend set that is never truly static. That is the backdrop for both NGINX Ingress Controller (NIC) and NGINX Gateway Fabric (NGF). In both cases, Kubernetes is the source of…